Why Businesses Must Take Control of Their Infrastructure After Software Development
After an external development team hands over your software, who controls your servers, databases, and sensitive credentials? Discover why businesses must secure their digital infrastructure, revoke unnecessary access, and establish independent ownership to protect their operations, customers, and future growth.
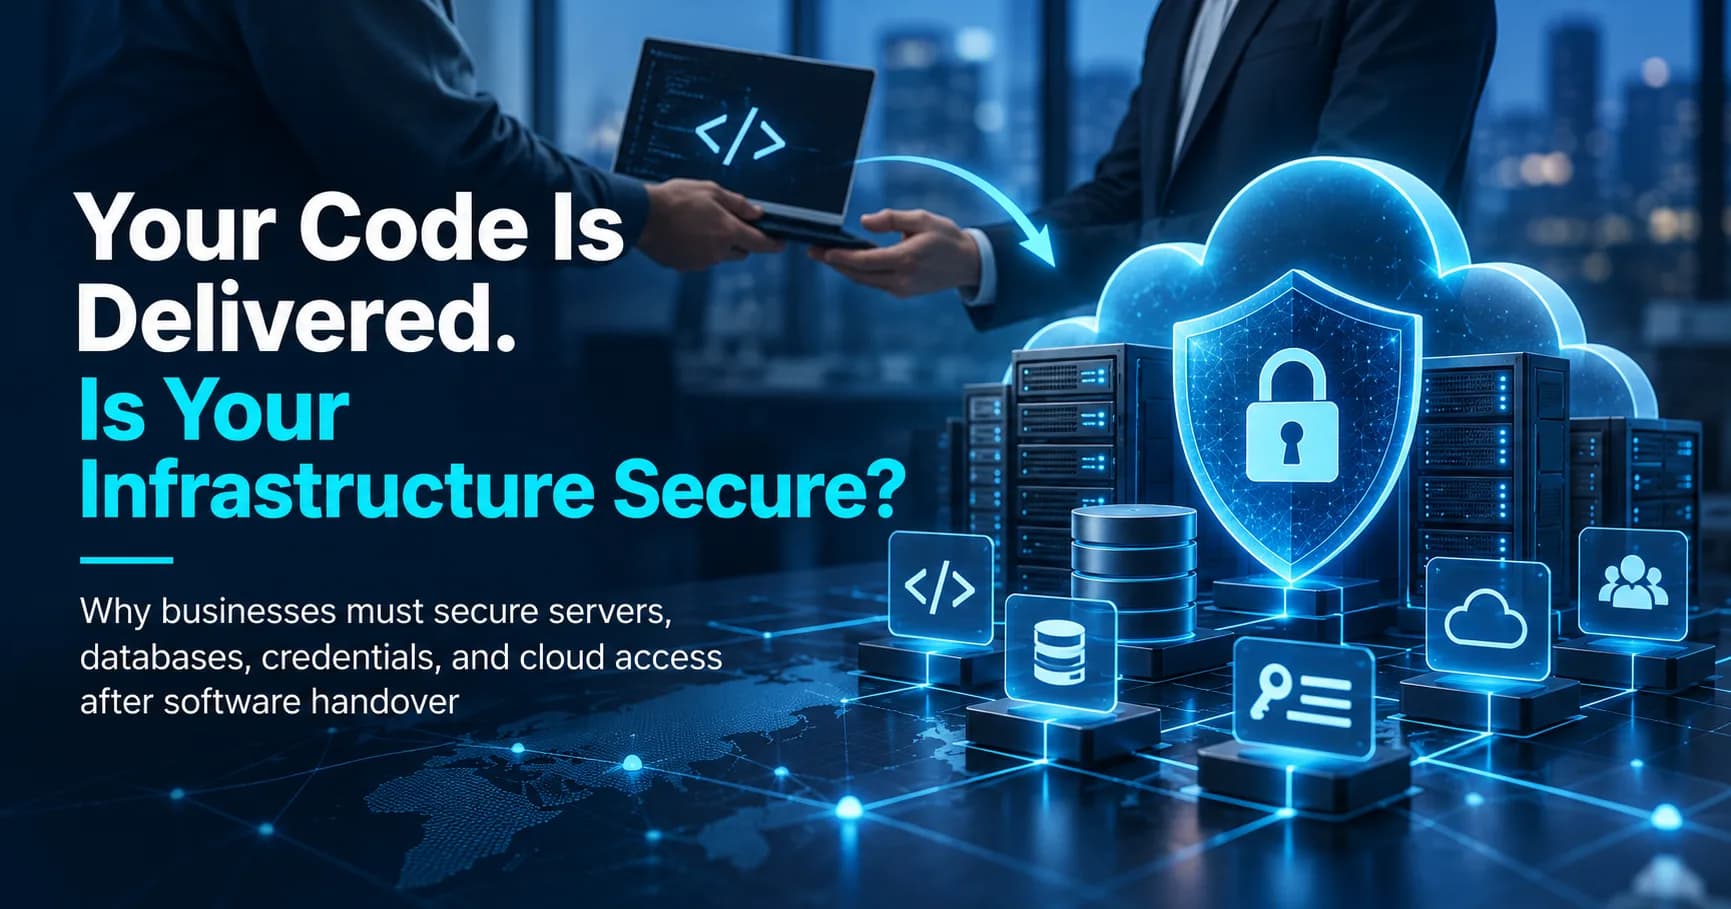
Why Businesses Must Take Control of Their Infrastructure After Software Development
Your developers may have finished building your software, but have you secured the infrastructure that keeps your business running?
Outsourcing software development has become a practical business strategy. Startups, established companies, financial institutions, and growing enterprises regularly hire external developers or software agencies to build websites, mobile applications, customer management systems, and other digital products.
This approach offers significant benefits. Businesses gain access to specialized technical expertise without necessarily maintaining a large internal development team.
However, one important responsibility is frequently overlooked: what happens to the infrastructure, credentials, and administrative access after the development team completes the project?
Many business owners believe that receiving their application's source code, documentation, and login credentials means they now have complete ownership and control.
Unfortunately, that assumption can create serious operational and security risks.
Source code is only one component of a software product. The infrastructure supporting that code—including servers, databases, cloud accounts, domain names, deployment systems, and third-party integrations—often determines who truly controls the application's operations.
This article explains why businesses must take responsibility for their digital infrastructure after software development, the risks of neglecting this responsibility, and the practical steps organizations should take to secure their technology investments.
1. Source Code Ownership Is Not the Same as Infrastructure Control
One of the most common misunderstandings in outsourced software development is the assumption that owning the source code automatically means owning the entire software system.
In reality, these are two different responsibilities.
What is source code?
Source code consists of the programming instructions written by developers to create an application.
For example, a business might receive the complete source code for its e-commerce platform, including its frontend interface, backend services, and database models.
However, the application might still depend on resources controlled by the development agency.
These could include:
Cloud hosting accounts and virtual private servers.
Production databases and database administration credentials.
Domain registrations and DNS management.
Application programming interface (API) keys.
Email delivery services and SMTP credentials.
Cloud storage accounts.
Payment gateway integrations.
Continuous integration and deployment systems.
Third-party authentication services.
Monitoring and error-reporting platforms.
If these resources remain under the developer's personal or agency-controlled accounts, the business may not have the level of independence it expects.
A practical example
Imagine a company hires an external development agency to build a customer-facing mobile application.
The agency delivers the complete source code and confirms that the project is finished.
However, the production database remains on a cloud account registered to the agency. The application's deployment system also uses credentials owned by one of the agency's employees.
The company may have legal ownership of the software under its contract, but it does not yet have independent operational control.
If the agency becomes unavailable, terminates its hosting arrangement, or experiences its own security incident, the company's services could be disrupted.
The lesson is simple: owning your software is important, but controlling the infrastructure that operates it is equally essential.
2. External Developers May Still Have Access After Project Completion
During software development, external teams often require significant access to company systems.
Developers may need permission to configure servers, connect databases, deploy applications, troubleshoot errors, and integrate third-party services.
These permissions are usually legitimate and necessary while the project is active.
However, problems arise when access remains unchanged after the work is completed.
For example, a former developer might still possess:
SSH keys allowing access to production servers.
Database usernames and passwords.
Administrator accounts on cloud platforms.
Deployment tokens stored on personal computers.
Access to private source code repositories.
API credentials used by production applications.
This does not necessarily indicate malicious intent. In many situations, access simply remains active because nobody formally reviewed it during handover.
Nevertheless, unnecessary access creates security exposure.
A former developer's device could later become compromised. Credentials stored on that device could potentially provide an attacker with access to the company's infrastructure.
The organization may have no immediate indication that its systems are being accessed using previously authorized credentials.
What businesses should do
Once development is complete, businesses should perform a formal access review.
Every person, account, service, and integration with access to production infrastructure should be identified.
Accounts that are no longer needed should be disabled or removed. Shared credentials used during development should be replaced, and necessary ongoing access should be reassigned through company-controlled accounts.
Where external maintenance is still required, businesses should provide restricted, individually identifiable access instead of permanent unrestricted administrator privileges.
Access should exist because it is currently necessary—not simply because it was granted during development.
3. Change and Secure Credentials Used During Development
Credentials are among the most sensitive components of any digital infrastructure.
They include passwords, API keys, authentication tokens, SSH private keys, and other secrets that provide access to applications and services.
During development, these credentials may be shared between developers, stored in configuration files, or temporarily copied to development environments.
Although professional teams should follow secure credential-management practices, businesses cannot assume that every credential remained restricted throughout the project.
The OWASP Secrets Management Cheat Sheet recommends establishing processes for securely storing, auditing, rotating, and revoking sensitive credentials.
Why credential rotation matters
Suppose an external developer configured a production database using a password also available in a shared development environment.
Even after the developer's administrative account is removed, anyone possessing that database password might still be able to access the database if network permissions allow it.
Revoking one user account does not automatically invalidate every credential that person previously used.
Businesses should therefore review and replace credentials that were shared unnecessarily, exposed, or retained outside approved company-controlled systems.
Particular attention should be given to:
Database credentials: Ensure production databases use dedicated accounts with only the permissions required by each application.
Server access: Remove unauthorized SSH keys, review privileged users, and restrict administrative access.
API keys: Replace exposed or widely shared credentials and limit each key to its intended function.
Cloud access tokens: Review permissions and revoke tokens associated with completed development activities.
Application secrets: Protect session-signing secrets and other sensitive application configuration values.
Some credentials, especially encryption keys and signing keys, require carefully planned rotation because replacing them incorrectly can interrupt operations or make existing encrypted information inaccessible.
The objective is not to change everything blindly. It is to establish a controlled and verifiable credential-management process.
4. Protect Customer Data and Confidential Business Information
For many organizations, the greatest risk of insecure infrastructure is the potential exposure of sensitive information.
Applications frequently process information such as customer names, email addresses, phone numbers, financial records, transaction histories, employee information, and confidential business documents.
Depending on the nature of the business, they may also process identity information or other highly sensitive personal data.
If production databases remain accessible through unnecessary accounts, weak credentials, or poorly configured network services, that information could be exposed.
Consider an online business
An e-commerce company commissions a developer to build its ordering and payment-management platform.
After delivery, the company receives the source code but does not review the database's network configuration.
The database remains directly accessible from the internet, and a previously shared administrative account is still active.
Even if the application itself has secure authentication, weaknesses in the underlying infrastructure could allow unauthorized access through a different route.
This illustrates an important cybersecurity principle:
Application security cannot compensate for every weakness in the infrastructure supporting the application.
Businesses should protect customer data through appropriate access controls, encrypted communications, secure storage, tested backups, and continuous monitoring.
They should also ensure that external developers do not retain unnecessary copies of production data after their contractual responsibilities have ended.
Where personal data is involved, organizations must consider applicable data protection laws and contractual obligations.
For Nigerian businesses, this includes assessing their responsibilities under the Nigeria Data Protection Act 2023 and relevant regulatory requirements.
5. Establish Clear Ownership of Cloud Accounts and Digital Assets
A company should not discover that it does not control its cloud infrastructure only when something goes wrong.
Unfortunately, this situation can occur when software projects are deployed using accounts created by external developers.
For example, a developer may register the company's domain name, create an AWS account, configure a virtual private server, or establish a cloud storage service using an agency-owned account.
The arrangement may work perfectly while the business relationship remains active.
Problems can arise when the company wants to change vendors, expand its infrastructure, audit its spending, or handle an urgent production incident.
The importance of business-controlled accounts
Critical infrastructure should be registered to and governed by the business wherever possible.
This includes:
Domain names: The business should control its domain registrar account, registration information, DNS records, and renewal arrangements.
Cloud platforms: Cloud accounts should belong to the company, with appropriate administrative and billing controls.
Source code repositories: The organization should control the main repository and define who can access, modify, and deploy code.
Database services: Production data should reside in infrastructure governed by the business or an authorized provider operating under clear contractual arrangements.
Third-party services: Payment processors, email services, storage providers, and monitoring tools should be connected through approved company-owned or company-controlled accounts.
Ownership should also include access recovery arrangements.
A business that relies on a single employee's personal email address to recover its infrastructure accounts may face significant operational challenges if that employee becomes unavailable.
Does the business need to manage everything internally?
Not necessarily.
A company can outsource infrastructure management to a specialist provider while retaining ownership, visibility, contractual safeguards, and administrative oversight.
The distinction is between delegating operational responsibilities and surrendering control of critical business assets.
6. Secure the Production Environment Before Declaring the Project Complete
Software that works correctly is not automatically secure.
A successful demonstration or user acceptance test confirms that certain features behave as expected. It does not establish that the entire production environment has been appropriately protected.
Infrastructure security requires separate verification.
For example, a newly deployed application might contain:
Unnecessary open network ports.
Default administrator accounts.
Outdated operating system packages.
Publicly accessible internal services.
Incorrect file and directory permissions.
Exposed configuration files.
Missing security updates.
Inadequate logging or backup arrangements.
Some of these weaknesses may not affect everyday application functionality.
The software can appear to operate normally while remaining exposed to avoidable threats.
Conduct a post-development security assessment
Businesses should arrange an assessment appropriate to the application's sensitivity and risk.
The assessment should examine the operating system, networking configuration, application services, database security, identity permissions, software dependencies, and deployment arrangements.
It should also consider whether development and production environments are properly separated.
The National Institute of Standards and Technology provides guidance through its Secure Software Development Framework, which encourages secure development practices, protection of software components, vulnerability management, and attention to software supply-chain risks.
For organizations handling sensitive information or supporting critical operations, independent security testing may be appropriate before final acceptance.
A production deployment should be treated as the beginning of ongoing operational security—not the end of security responsibilities.
7. Maintain Backups That the Business Can Independently Restore
Backups are essential for business continuity.
Yet many organizations assume their development team or hosting provider has already configured everything necessary.
That assumption can prove costly.
An application may have a database backup running periodically, but the backup might be stored on the same server as the production database.
If the server is compromised or its storage fails, both the original data and its backup may be lost.
Alternatively, backups may exist in a cloud account the company cannot access independently.
What a reliable backup arrangement should include
Businesses should establish backup procedures that reflect the importance of their data and services.
Important considerations include:
Automated backups at appropriate intervals.
Encrypted backup storage.
Copies stored separately from production systems.
Restricted access to backup repositories.
Defined data retention periods.
Recovery procedures documented for authorized personnel.
Periodic restoration tests.
An especially important distinction is that a backup is not fully dependable until its restoration process has been tested.
Businesses should verify that they can recover both application data and the configuration needed to resume operations.
For example, restoring database files alone might not restore a functioning application if the company has lost its encryption keys, environment configuration, or deployment instructions.
Proper infrastructure handover should therefore include documented and tested recovery procedures.
8. Implement Continuous Monitoring and Security Logging
Once software enters production, it becomes part of the organization's ongoing operations.
Servers may fail, storage capacity may become exhausted, services may stop responding, and security threats may emerge.
Without monitoring, businesses often discover these problems only after customers begin complaining.
Why monitoring matters
Infrastructure monitoring helps organizations identify operational problems before they cause prolonged disruption.
Depending on the application's architecture, monitoring may include:
Availability monitoring: Check whether websites, applications, and APIs remain accessible.
Server resource monitoring: Track CPU usage, memory consumption, disk capacity, and other important performance indicators.
Database monitoring: Identify connectivity problems, unusual activity, and resource constraints.
Security logging: Record relevant authentication activity, administrative actions, and suspicious access attempts.
Certificate monitoring: Track TLS certificate validity and renewal status.
Backup monitoring: Detect failed backup jobs and incomplete recovery processes.
Incident alerting: Notify responsible personnel when an event requires investigation.
Monitoring is most effective when alerts are actionable and someone has clear responsibility for responding.
An alert that nobody receives or understands offers limited operational value.
For businesses without a dedicated IT department, a managed monitoring service can provide visibility while keeping day-to-day responsibilities clearly assigned.
9. Reduce Dependency on a Single Development Agency
Outsourcing development should not create permanent technical dependency.
A business should be able to continue operating its software even when the original development team is unavailable.
This ability is sometimes described as operational independence or vendor portability.
Consider a company that has invested heavily in a custom business platform.
The software performs well, but the original agency controls the deployment process, database credentials, and cloud account.
When the company hires a new development team, the incoming engineers cannot access the required infrastructure.
The business must then spend additional time and money recovering access, rebuilding environments, or migrating services.
These problems can delay product improvements and create unnecessary disruption.
How to maintain independence
A professional handover should include adequate technical documentation.
At a minimum, the organization should receive:
Complete source code and repository access.
System architecture and infrastructure documentation.
Deployment and rollback procedures.
Database structure and migration instructions.
An inventory of external dependencies.
Environment configuration guidance without exposing secrets unnecessarily.
API integration documentation.
Backup and restoration procedures.
Operational troubleshooting guidance.
A clear record of infrastructure ownership and administrator permissions.
Where practical, the organization should demonstrate that an authorized replacement team can deploy, maintain, and recover the application without relying on undocumented knowledge held by the original developers.
This does not eliminate the value of long-term vendor relationships.
Instead, it creates a healthier relationship built on service quality rather than technical dependency.
10. Infrastructure Security Is a Business Responsibility, Not Just an IT Task
Infrastructure management is often viewed as a purely technical concern.
However, its consequences extend into finance, legal compliance, customer trust, and overall business continuity.
A major infrastructure failure can prevent customers from accessing essential services.
A security incident may expose confidential data, interrupt transactions, or create regulatory and contractual obligations.
Weak infrastructure ownership arrangements can also complicate investment due diligence, business acquisitions, audits, and technology migrations.
The role of business leadership
Business owners and executives do not need to personally configure firewalls or administer production databases.
They do, however, need to ensure that qualified individuals or service providers are responsible for those activities.
Management should understand:
Who owns the infrastructure?
Who can access production systems?
Who approves important changes?
Who monitors security and availability?
Who is responsible when an incident occurs?
Can the business recover its systems without the original development team?
These questions establish accountability.
Cybersecurity frameworks such as CISA's Cybersecurity Performance Goals emphasize governance, asset identification, protective safeguards, threat detection, incident response, and recovery.
The underlying principle is that technology security requires ongoing organizational responsibility.
11. A Practical Infrastructure Handover Checklist
Businesses should incorporate infrastructure ownership and security requirements into their software acceptance process.
The following checklist provides a practical starting point.
Phase 1: Verify ownership
Confirm that the business controls its source code, cloud accounts, domains, databases, production environments, and essential third-party services.
Document which assets are owned directly and which are operated by contracted providers.
Phase 2: Audit access
Identify all users, service accounts, SSH keys, API tokens, and administrative permissions.
Remove unnecessary access and establish clearly defined permissions for retained service providers.
Phase 3: Secure credentials
Review secrets used during development.
Revoke credentials that should no longer exist, replace those with unnecessary exposure, and store production secrets through an approved secure management process.
Phase 4: Assess infrastructure security
Review exposed services, firewall policies, system updates, database access restrictions, application configuration, and known vulnerabilities.
Arrange additional security testing where the business risk warrants it.
Phase 5: Verify backups and recovery
Confirm that essential data is backed up, backups are appropriately protected, and restoration procedures have been tested.
Ensure that the business has independent access to its recovery arrangements.
Phase 6: Establish monitoring
Implement appropriate availability, performance, and security monitoring.
Define who receives alerts and who is responsible for investigating them.
Phase 7: Complete documentation
Obtain architecture diagrams, deployment instructions, maintenance procedures, integration details, and operational documentation.
Ensure that the business can maintain the platform without relying exclusively on the original developers.
Phase 8: Assign ongoing responsibility
Designate an internal team, infrastructure specialist, or managed service provider to maintain the environment.
Establish procedures for security updates, access reviews, backups, monitoring, and incident response.
These activities should not be postponed indefinitely after launch. Critical security and ownership requirements should ideally be included in project contracts and completed as part of formal acceptance.
12. Should Businesses Host Their Applications on Their Own Servers?
An important question is whether companies should maintain their own physical servers, rent virtual private servers, or use managed cloud platforms.
There is no universal answer.
The appropriate hosting arrangement depends on several factors, including the organization's technical capacity, security requirements, budget, application architecture, and availability expectations.
Self-managed infrastructure
Self-managed servers provide flexibility and direct control over system configuration.
However, the business or its appointed infrastructure administrator must manage operating system updates, network security, backups, monitoring, and other operational responsibilities.
This approach may suit organizations with sufficient technical expertise or a trusted infrastructure management partner.
Managed cloud infrastructure
Managed cloud services can reduce some operational responsibilities by allowing providers to manage selected infrastructure components.
However, the customer remains responsible for important areas such as account security, access permissions, application configuration, and the protection of its information, depending on the service model.
Dedicated infrastructure management providers
Businesses can also engage specialized infrastructure teams to manage deployment, server security, monitoring, backups, and maintenance.
This option can be particularly useful for organizations that outsource application development but do not maintain a full internal infrastructure team.
The central consideration is not whether the company physically owns its servers.
What matters is that the business retains appropriate ownership, governance, access, visibility, and recovery capabilities.
13. Treat Software Handover as a Security and Operational Milestone
Software projects frequently measure completion through feature delivery.
The login system works. Customers can place orders. Payments can be processed. Reports display correctly.
These achievements matter, but they are only part of a successful project.
A professional software handover should establish that the business can operate the completed system securely and independently.
For this reason, companies should agree on handover requirements before development begins.
Contracts should clearly address source code ownership, intellectual property rights, hosting arrangements, access transfer, documentation, credential management, security responsibilities, and post-development support.
Depending on the nature of the project, businesses may also require a defined transition period during which the external team assists with access migration, infrastructure verification, and operational knowledge transfer.
This helps prevent rushed handovers and reduces uncertainty about responsibilities.
Most importantly, it ensures that infrastructure security is planned from the beginning rather than treated as an unexpected expense after deployment.
Conclusion: Your Software Is an Investment—Protect the Infrastructure Behind It
Hiring an external development team can be an effective way to transform a business idea into a functional digital product.
But delivering the source code should not mark the end of the company's involvement in securing the technology.
A business must understand who controls its servers, databases, credentials, cloud services, and deployment processes.
It must also establish appropriate safeguards, reliable backups, continuous monitoring, and clear operational accountability.
External development teams are not inherently a security risk. Many follow strong engineering practices and provide excellent long-term support.
The real problem arises when important ownership and security responsibilities remain undefined after delivery.
Organizations that address these issues early are better positioned to protect customer information, prevent avoidable disruption, work with future development partners, and scale their platforms confidently.
The most important question after receiving your source code is not simply, "Does the application work?"
It is, "Do we have secure, independent control over everything required to keep it working?"
A successful handover delivers more than software.
It delivers control, accountability, security, and business continuity.
About the author
Softon Digital Team
The Softon Digital team writes about software development, AI automation, product engineering, digital transformation and the practical technology decisions behind modern business systems.
- Cybersecurity
- infrastructure security
- software development
- software handover
- cloud security
- data protection
- business security
- source code ownership
- server management
- DevOps
- IT infrastructure
- software outsourcing